State-linked hackers are increasingly using public blockchains to keep malware connected to infrastructure that traditional takedowns cannot easily disable.
Groups tied to North Korea and Iran accounted for roughly two-thirds of newly observed blockchain-dead-drop activity each quarter by the second quarter of 2026, Chainalysis said. State-linked operators now represent about half of all activity the analytics firm tracks, up from a negligible share in early 2024.
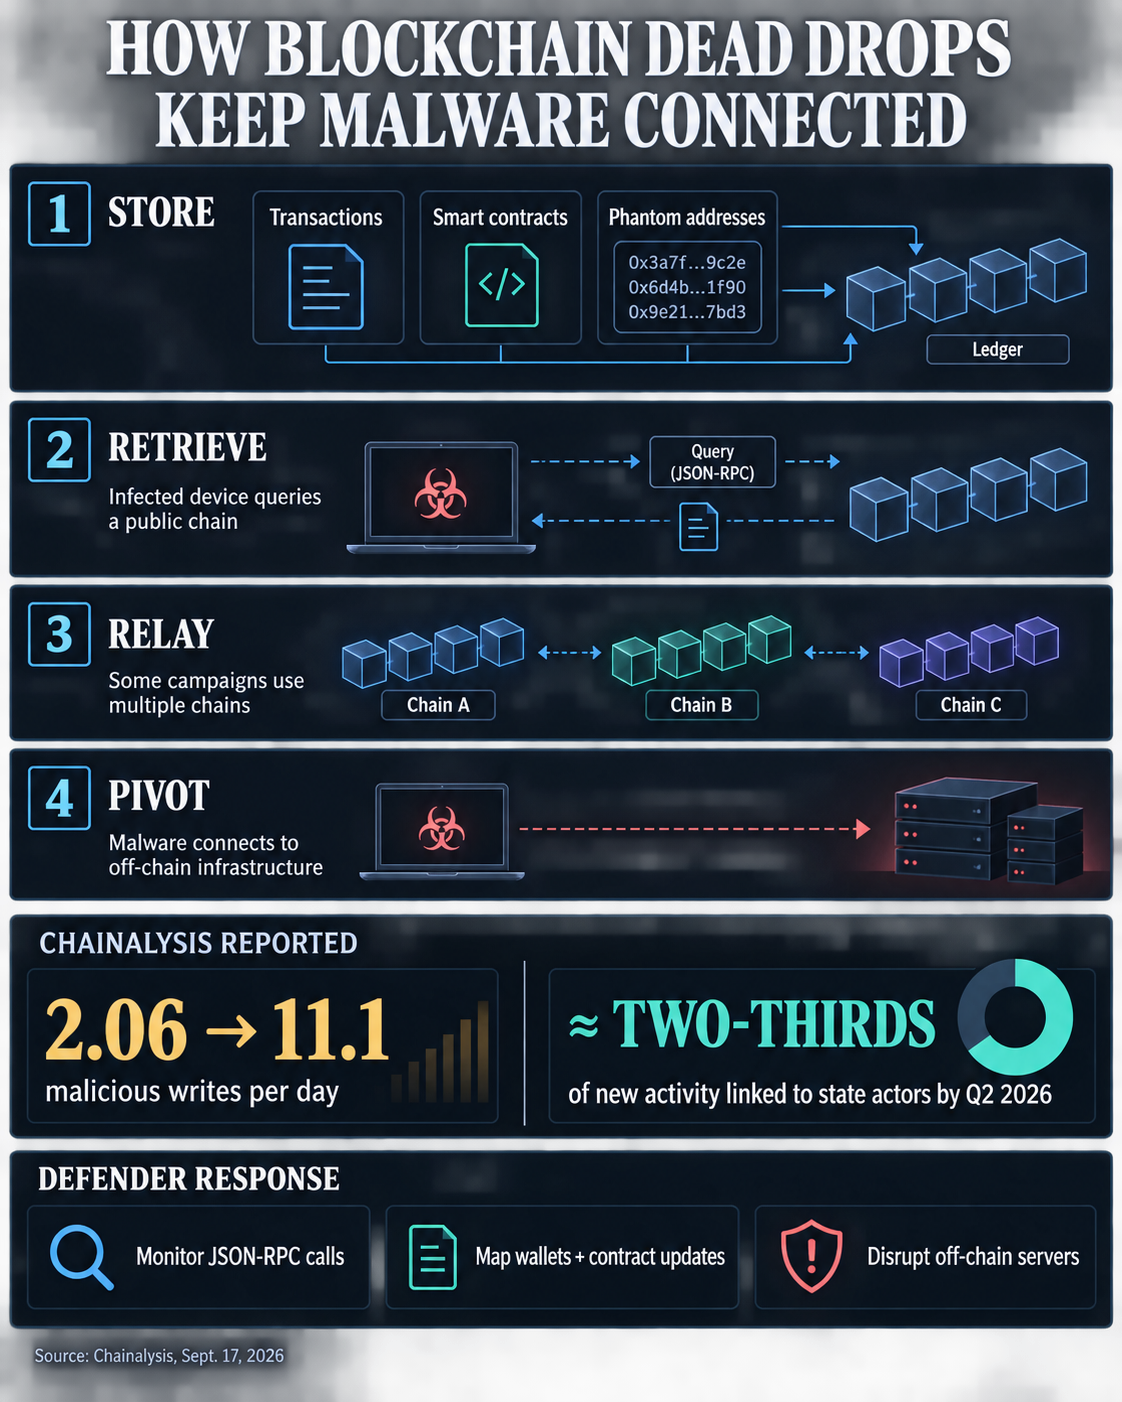
The technique, known as a blockchain dead drop, stores malware instructions, command-and-control addresses or pointers inside transactions and smart contracts. Compromised devices can repeatedly query those public records for updated instructions, letting attackers change servers without reinfecting victims.
Chainalysis said malicious blockchain writes rose from 2.06 a day to 11.1 after the emergence of high-capacity open-weight Chinese artificial-intelligence models, a 440% increase in less than a year.
The firm said those models lowered the expertise required to build the infrastructure, though its measurement does not identify a single model or establish that AI alone caused the increase.
The shift adds another security challenge for crypto companies, developers and enterprises that increasingly rely on public chains for legitimate applications. Blocking access to an entire network would also disrupt wallets, decentralized-finance platforms and other services using the same infrastructure.
North Korea adds cross-chain redundancy
North Korean-linked operators are already showing how blockchain infrastructure can make a malware campaign more resilient after defenders identify its components.
Chainalysis connected the threat group UNC5342 to a previously unattributed setup that uses TRON and Aptos as redundant routes into BNB Smart Chain. Encoded pointers on the first two networks direct infected devices toward malware instructions stored on BSC. The malware queries TRON first and switches to Aptos if that route fails.
Attackers can rotate their off-chain infrastructure by posting another transaction, after which previously infected machines automatically retrieve the updated location. Chainalysis said disrupting the operation would require action across all three chains at the same time.
Google Threat Intelligence began tracking UNC5342 in February 2025, when it used blockchain-based malware delivery in fake-job campaigns aimed at cryptocurrency and technology developers. The group used smart contracts to help deliver credential-stealing malware targeting browser data, passwords, and crypto wallets.
The approach extends a tactic attackers adopted after conventional hosting providers began shutting down malicious infrastructure. EtherHiding campaigns appeared on EVM-compatible networks in 2023 after operators shifted code into smart contracts that could remain accessible even when websites or servers were removed.
Iran-linked operators have taken a different route. Chainalysis said suspected actors connected to Iran's Ministry of Intelligence have embedded command-and-control routing information inside Bitcoin transactions sent to a well-known address historically associated with Satoshi Nakamoto. The address itself has no connection to the attackers and functions as a permanent public reference point for infected machines.
AI lowers the barrier for smaller operators
The same techniques are spreading beyond state-backed groups as artificial-intelligence coding tools reduce the specialist knowledge once required to build blockchain-based command infrastructure.
Chainalysis said it now tracks blockchain-dead-drop activity across five major networks and more than a dozen named malware strains. Russian-language criminal groups have also deployed smart contracts on Polygon as command resolvers, with infrastructure marketed to other operators through a malware-as-a-service model.
That creates a path for attackers to rent blockchain-based infrastructure rather than design it themselves.
In one operation, Chainalysis identified a primary wallet controlling multiple resolver contracts, with individual contracts apparently serving separate customers or campaign variants. Related addresses were also linked to fraudulent tokens and clipboard-hijacking campaigns targeting crypto users.
The economics favor continued adoption. Posting small amounts of data on public chains can be inexpensive, while the underlying record remains globally available and hard to remove. Attackers can then keep most of the actual compromise off-chain, using the ledger primarily to tell infected machines where to connect next.
Defenders shift from takedowns to surveillance
The permanence that gives attackers resilience also leaves a record that cybersecurity teams can monitor.
Every transaction used to rotate infrastructure remains timestamped and publicly visible. Chainalysis said defenders can map operator wallets, resolver contracts, funding relationships, and update histories, potentially linking campaigns that would appear unrelated when viewed only through their domains or servers.
Organizations can also monitor outbound JSON-RPC requests, the calls software uses to query blockchain nodes, for signs that infected machines are contacting suspicious contracts or addresses. Centralized API providers and RPC gateways remain potential intervention points even when the underlying blockchain cannot be taken offline.
Protocol developers have limited options to remove the underlying capability without restricting legitimate blockchain use. Chainalysis said preventing arbitrary data from being written on-chain would require changes with consequences that could outweigh the security benefit.
That leaves exchanges, infrastructure providers and cybersecurity firms with a growing monitoring problem. As more malware treats public chains as persistent coordination layers, defenders will need to follow activity across wallets, contracts and multiple networks while preserving access for legitimate users.
The next pressure point is likely to fall on RPC and API providers sitting between infected devices and blockchains. Their ability to identify and block malicious queries without disrupting ordinary applications could determine how much of the attackers' new resilience survives once the technique becomes more widely tracked.
The post Blockchain malware activity jumps 440% as AI lowers the barrier for North Korea and Iran-linked hackers appeared first on CryptoSlate.